
AgentOps
AI Control Plane: governing agents across multiple platforms
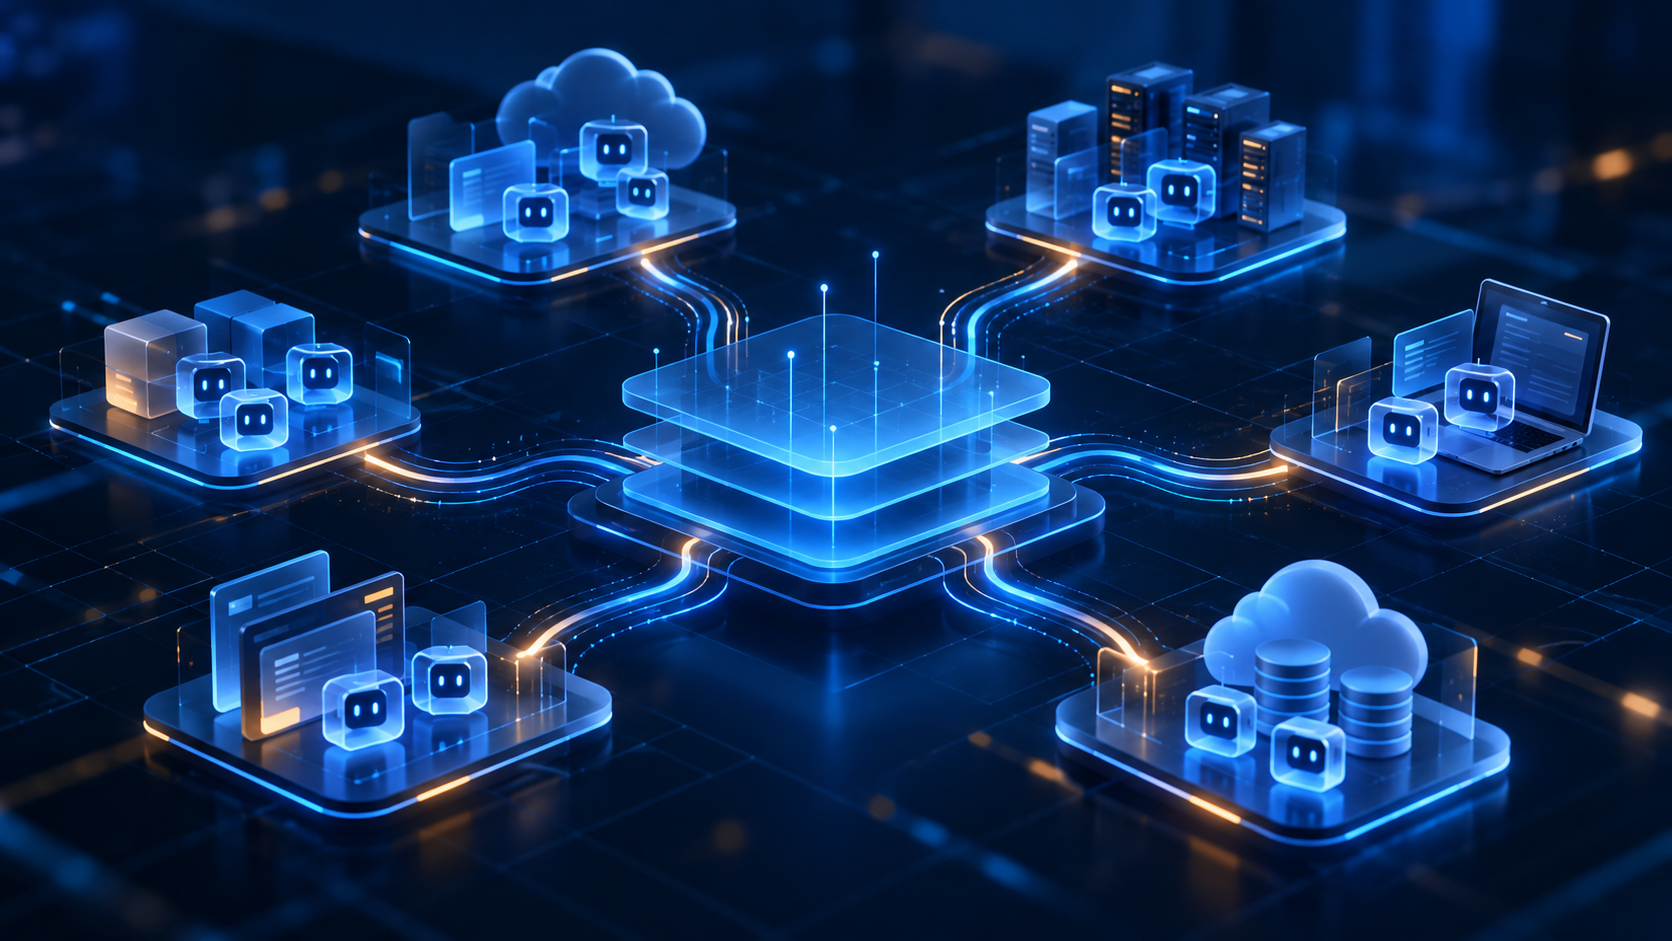
A company may use artificial intelligence agents developed in-house, others embedded in corporate applications, and still contract solutions from different vendors. Each platform offers its own administration, monitoring, and security mechanisms.
This diversity makes it possible to take advantage of specialized technologies, but it also creates a challenge. How do you keep control over all these agents when each one operates in a different environment?
The scale of this problem already shows up in large organizations. In August 2026, Microsoft reported that its internal technology team had achieved visibility into more than 500,000 AI agents, using a management layer that gathers information on usage, categories, and owners [1].
The number reflects Microsoft’s specific experience, not the average reality of companies. Still, it helps illustrate how agent management can reach a scale that is hard to handle with isolated tools.
This is the context in which the concept of an AI Control Plane, or control plane for artificial intelligence agents, gains importance.
The idea is to establish a common layer of visibility and governance, able to track agents distributed across different platforms and support the application of consistent corporate controls.
The challenge is not necessarily to bring all agents together on a single platform, but to ensure the company can govern them in an integrated way, a topic related to AI Agent Sprawl.
What an AI Control Plane is and why it becomes necessary
Traditionally, companies use different tools to manage applications, identities, infrastructure, security, and business processes.
With the arrival of AI agents, a new element appears in this operation. Besides querying information and producing answers, agents can use tools, interact with corporate systems, and execute actions with different levels of autonomy.
This widens the need to understand not only which agents exist, but how they are acting and which limits they must respect.
An AI Control Plane seeks to meet this need by offering a common structure to organize controls, track behaviors, and establish policies for the operation of agents.
The concept is already present in the strategies of large vendors. In July 2026, IBM introduced its Agentic Control Plane, associated with watsonx Orchestrate, with a proposal to bring together operation, governance, and tracking capabilities for agents in enterprise environments [2].
Microsoft also works with this approach through Agent 365, aimed at the corporate administration and governance of agents, and the Foundry Control Plane, aimed mainly at teams responsible for the development and technical operation of these applications [3].
These examples show that the term can take on different scopes, depending on the architecture and the responsibilities covered.
The common principle lies in the need to offer a more consistent view of how agents operate.
As agents gain autonomy, governance stops depending only on individual settings and starts requiring controls that work across platforms, teams, and processes.
This does not mean all functionality must be gathered in a single solution. A control architecture can integrate existing capabilities and establish a shared view, preserving the responsibilities of each tool.
What to centralize and what to keep distributed
One of the main decisions in building an agent governance architecture is defining which information and controls need to be shared across the organization.
Consider a company that uses agents in customer service, finance, and IT operations. Each area can choose technologies suited to its needs, but the organization still needs consistent answers about who answers for these agents, which resources they use, and how their actions are tracked.
In this scenario, it makes sense to establish a corporate view that relates agents, owners, usage policies, permissions, operational events, and resource consumption.
However, this view does not necessarily require all activities to be executed by the same platform.
Identity administration can remain in existing corporate systems. Data protection stays tied to security tools, while task processing can occur in the environments chosen by each application.
The role of a common control layer is to help these capabilities work in a coordinated way, preventing each environment from developing its own governance mechanisms without considering the rest of the organization.
An analysis published by IBM in September 2026 reinforces this need when discussing the use of agents provided by third parties. The company highlights that trust in a given vendor should not represent unrestricted authorization for all the agents it provides [4].
An agent responsible for querying public information presents different risks from another agent authorized to modify financial records or execute transactions.
Governance therefore needs to consider the purpose, autonomy, and potential impact of each agent, regardless of its origin.
Centralizing governance does not mean centralizing all execution, as we discussed in agentic AI governance. It means establishing common criteria to control agents that continue to operate in different environments.
This distinction also helps avoid an undesired consequence: creating a new isolated platform that, instead of reducing fragmentation, adds another layer of complexity to the operation.
How to keep control when agents gain autonomy
Knowing the agents and tracking their activities is necessary, but not sufficient when they start executing actions in corporate systems.
Imagine a customer service agent authorized to look up orders and offer alternatives to resolve complaints. In a given situation, it identifies the possibility of granting a refund.
The company can establish that operations above a certain amount depend on human approval.
In this example, there are two different needs. The first is to track the decision and record what happened. The second is to ensure that the established policy is respected before the transaction is executed.
This difference between observability and effective enforcement of controls is highlighted by IBM in its analysis of governing third-party agents [4].
Observability makes it possible to understand the agent’s behavior, identify events, and investigate problems. Governance also needs to define which actions are allowed, under which conditions, and how any restrictions will be applied.
The challenge increases when different platforms take part in the same process. An agent can request information from another, use an external tool, and forward an action to a corporate system.
In this scenario, controls need to consider the chain of interactions, and not just the isolated behavior of each agent.
Microsoft’s Cyber Pulse 2026 report shows that this concern is already part of corporate security initiatives. According to the data presented, 47% of the organizations surveyed were implementing specific security controls for generative AI [5].
The indicator does not represent agent governance exclusively, but it shows that AI adoption is accompanied by a growing need to establish specific protection and control mechanisms.
Microsoft’s internal experience also offers an important observation. By expanding visibility into its agents, the company identified situations such as agents without clearly defined owners, duplications, and risks associated with using different platforms [1].
These problems show that control does not end when an agent is put into production. The company needs to track its usage, its changes, and its participation in processes over time.
The greater the agents’ autonomy, the more important it becomes to combine operational visibility, consistent policies, and the ability to intervene.
An AI Control Plane can contribute to this organization, as long as its responsibilities are clearly defined and its controls are compatible with the platforms and systems involved.
The goal is not to eliminate technological diversity, but to let it evolve without compromising the governance of the operation.
From vision to practice: ARGUS
The growth of AI agents across different platforms reinforces the need for an operational view that goes beyond the limits of each tool or department.
This is the context in which ARGUS, the Operational and Agentic Intelligence platform from Target Solutions, contributes to corporate operations.
Through its AgentOps capabilities, ARGUS supports the orchestration, monitoring, observability, and governance of AI agents, offering visibility into their activity across different environments.
The AI Gateway layer complements this proposal, contributing to policy enforcement, access control, and tracking of AI resource consumption.
By connecting agents, people, and tools in a shared operational context, the platform helps organizations better understand how their agents interact with the operation and establish controls compatible with their needs.
This approach makes it possible to preserve the tools and platforms the company already uses, without requiring their replacement for the AgentOps capabilities to be put to use.
The proposal of ARGUS is to support the evolution of agent autonomy with more visibility, coordination, and governance, helping AI expansion happen in a controlled way.
Learn about ARGUS and see how it works in practice.
About the author
Paulo Florêncio de Menezes is an entrepreneur, partner, and co-founder of companies such as Target Solutions, BiPTT, and ARGUS.
He holds a degree in Data Processing from the Federal University of Amazonas (UFAM), an MBA in Business Management from Fundação Dom Cabral (FDC), and a Professional Master’s in Economics from Fundação Getulio Vargas (FGV).
In his Master’s research, he developed the IBEOP-IA (Brazilian Index of Potential Occupational Exposure to Artificial Intelligence), investigating the potential exposure of Brazilian occupations to AI capabilities by combining occupational data, artificial intelligence patents, and natural language processing techniques.
References
[1] Microsoft. Implementing Agent 365: How We’re Governing and Managing AI Agents at Microsoft. Aug. 6, 2026.
[2] IBM. Agentic Control Plane in IBM watsonx Orchestrate: One Place to Control Every AI Agent. Jul. 2, 2026.
[3] Microsoft. Foundry Control Plane and Agent 365: Two Control Planes Walk Into an Enterprise. 2026.
[4] IBM. How to Effectively Govern Third-Party AI Agents Across the Enterprise. Sep. 22, 2026.
[5] Microsoft. Cyber Pulse: An AI Security Report. Feb. 10, 2026.