AgentOps
AI agent governance: where to start and when to expand?
Governing artificial intelligence agents can seem like a task that requires, from day one, a complete corporate policy, a definitive architecture, and controls prepared for every possible scenario.
This expectation often creates two problems. Some organizations postpone any initiative until every answer is available. Others begin experimenting without defining owners, limits, or criteria to stop execution.
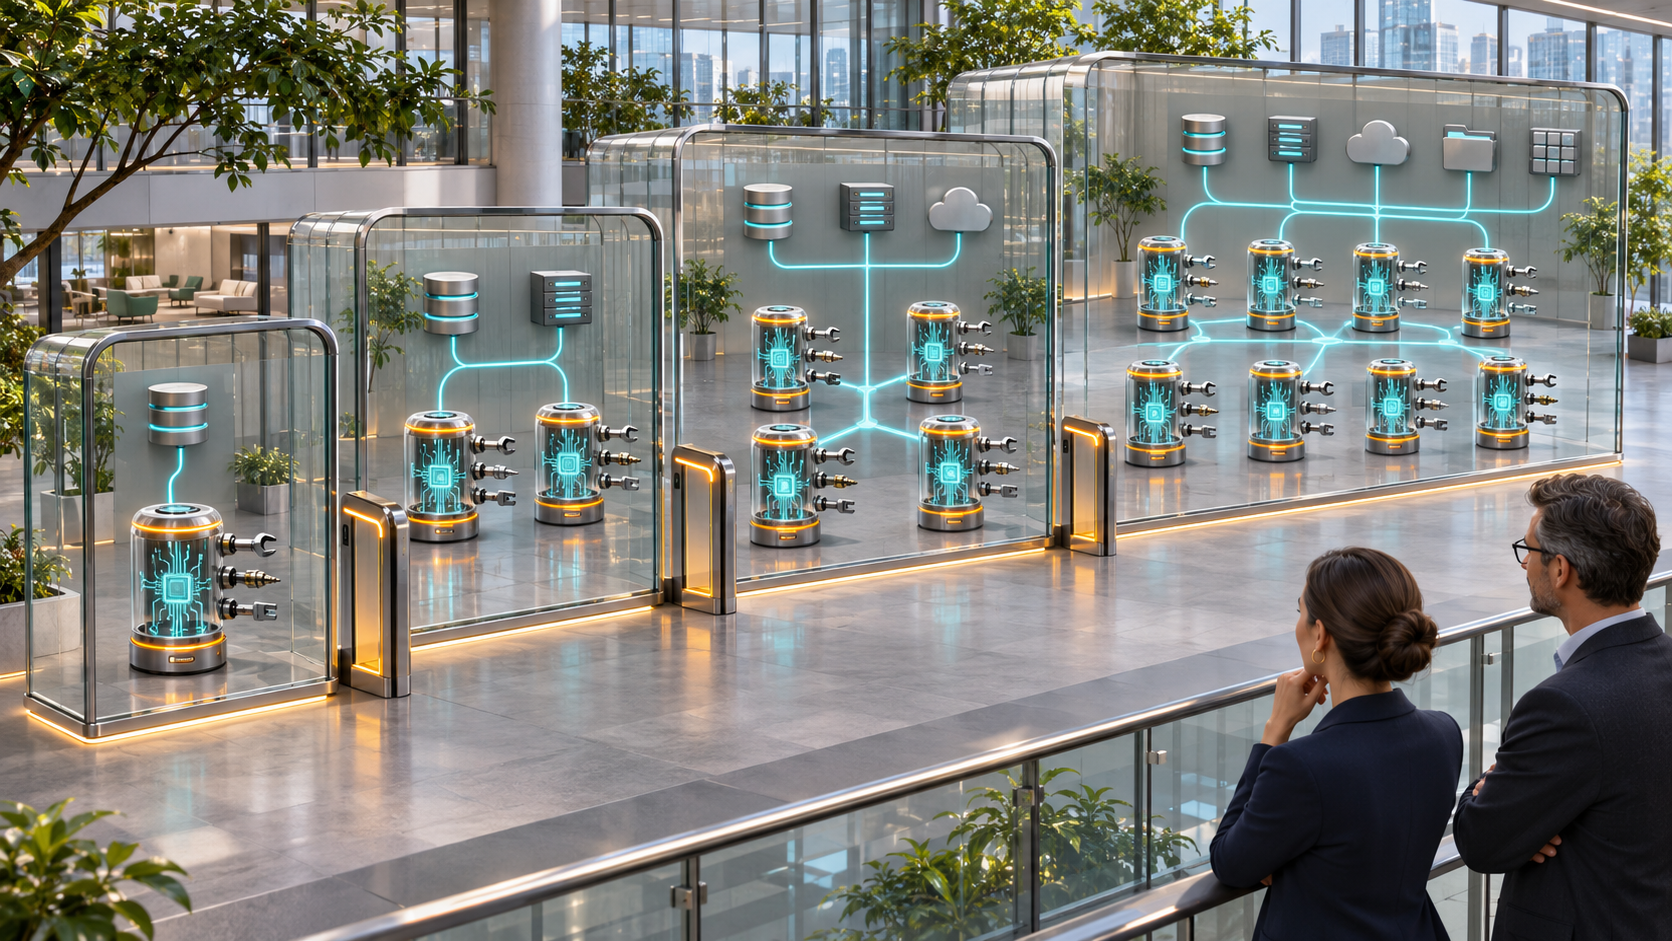
A more practical path exists. Governance can start with a delimited flow, rules proportional to risk, and enough evidence to decide whether the agent should remain restricted, be adjusted, or advance to a new stage.
Gradual deployment does not mean operating without control. It means increasing autonomy, scope, and integration only when the organization can demonstrate that it learned to supervise the previous stage.
Why start small
AI agents do not produce only responses. Depending on their configuration, they can consult data, access tools, start tasks, and change systems. The greater their autonomy, the more important it becomes to define who is accountable for the agent, which actions are authorized, and how operation will be monitored.
A global Deloitte survey with business and technology leaders indicated that only 21% of participating organizations considered their governance model for agentic AI mature [1]. The figure does not mean everyone should wait until reaching full maturity. It shows that rapidly expanding an initiative can put scale ahead of supervision capacity.
Starting with a known-scope process allows observing the agent under real conditions without exposing the entire organization at once. It also makes it easier to distinguish problems of the model, data, integrations, permissions, and the process design itself.
Gradual deployment begins before the pilot
The first step is not choosing the tool. It is selecting a flow in which objective, owner, and limits can be described clearly.
A good initial candidate has identifiable inputs, verifiable output, and controlled consequence. It should also allow human review when there is doubt or exception. Processes with irreversible decisions, high impact on people, or broad access to critical systems require greater preparation and may not be suitable for the first deployment.
Before starting the pilot, the organization needs to answer simple but decisive questions. What problem should the agent solve? Who is responsible for the outcome? Which data and systems may it access? Which actions may it execute? When should it request approval? How will its activity be recorded? What will make the team stop use?
These answers form an initial operational contract. It does not need to anticipate the entire corporate policy, but it must be specific enough to guide configuration, testing, supervision, and decision.
Five stages to expand with control
Deployment can advance in five stages, with explicit criteria between them.
-
Identify and delimit. Record objective, owner, users, data, integrations, permitted actions, and consequences of a failure. At this stage, the organization also defines what will not be delegated.
-
Test in a controlled environment. Assess the agent with representative cases, including common situations, exceptions, and inadequate inputs. The goal is not to prove it will never fail. It is to understand how it fails, what evidence it produces, and when it needs human intervention.
-
Operate with restricted scope. Release the agent to a limited group, process, or volume. Permissions should follow least privilege necessary. The team tracks results, deviations, interventions, accesses, and effects on involved systems.
-
Review and decide. Compare observed behavior with criteria defined before the pilot. The decision may be to expand, keep scope, reduce autonomy, correct design, or end the initiative.
-
Expand in layers. Increase users, volume, integrations, or autonomy separately. Each increase changes risk and should trigger a new verification, even when the agent already demonstrated good performance in the previous stage.
This logic avoids treating the pilot as permanent authorization. A solution approved to suggest an action is not automatically approved to execute it. An agent validated in one area is also not automatically authorized to operate in another, with different data, rules, and impacts.
Governance proportional to risk and autonomy
NIST organizes AI risk management into four connected functions: govern, map, measure, and manage [2]. In practice, this means policies and responsibilities need to connect to use context, assessments performed, and decisions made during operation.
For agents, control intensity should follow at least four dimensions: autonomy, access, consequence, and reversibility.
An agent that consults public information and prepares a draft requires a different level of supervision than one that accesses internal data, updates records, or triggers vendors. The same technology can occupy very different risk positions depending on task and permissions received.
PwC recommends treating agents as participants in a digital workforce, with identity, role, specific permissions, and auditable records. Human supervision should increase as autonomy and consequence of actions grow [3].
This helps avoid two extremes. The first is applying the same heavy process to any experiment, even low risk. The second is using initial classification as justification to reduce controls while the agent gains new capabilities.
What to observe during operation
Gradual deployment needs to produce evidence for the next decision. Assessing only final response quality is insufficient.
It is necessary to track which tasks were executed, which models and tools were used, which permissions were triggered, where failures occurred, and how often a person needed to review, correct, or take over the activity. Cost, execution time, and effects on systems that participate in the process also matter.
Criteria do not need to be identical for all agents. A support agent may be assessed mainly by usefulness and rework. An agent that executes actions needs to demonstrate, beyond quality, that it respects limits, produces traceability, and stops the flow when it encounters unauthorized conditions.
This observation turns governance into operational routine. Without it, the organization may maintain well-written policies and still not know how the agent behaves in production.
When not to expand
Expanding is not the only measure of success. Keeping an agent in restricted scope may be the correct decision when it generates value but still depends on frequent supervision. Ending a pilot can also prevent a design problem from turning into operational risk.
Expansion should stop when there is no clear owner, when permissions exceed task need, when records do not allow reconstructing an execution, or when exceptions depend on improvisation. The same applies when the team cannot distinguish agent failures from problems in data, integrations, or services that sustain the process.
A BCG study on AI assurance in the public sector highlights the importance of proportional criteria, usable responsibilities, and assessment throughout the lifecycle, instead of a static approval concentrated at the beginning [4]. Although the research context is governmental, the idea is useful for companies: each relevant change in use should renew analysis, not automatically inherit prior authorization.
From defined governance to operational supervision: ARGUS
As deployment advances, governance needs to leave documents and appear in operation. ARGUS can support this stage as an AgentOps platform, centralizing information from agents integrated into the environment and connecting identity, version, dependencies, and operational context.
With monitoring, orchestration, and governance, ARGUS can help track executions, interactions with models and tools, consumption, failures, and other indicators available in each implementation. This visibility helps compare observed behavior with limits defined for each deployment stage.
AI Gateway resources can also support applying access policies to integrated models and recording interactions. Business rules, risk criteria, and the decision to expand autonomy remain organizational responsibilities.
ARGUS does not replace organizational diagnosis, process design, definition of owners, or governance preparation. Its contribution begins when agents are integrated into the monitored environment and the organization needs to turn its decisions into continuous operational supervision.
About Target Solutions
Target Solutions has spent more than 15 years supporting organizations in evolving their infrastructure, monitoring, observability, automation, and operational intelligence operations.
Throughout this journey, it has participated in projects in complex environments in Telecom, Technology, Government, Energy, and large companies, contributing to increase operational efficiency and service reliability.
With the advance of AI agents, this experience also supports preparing organizations to adopt, govern, and operate this new class of technology.
We believe gradual deployment needs to combine organizational decision, technical preparation, and operational evidence. Expanding an agent’s scope without increasing supervision capacity can transfer speed to the process and uncertainty to operation.
Beyond the platform, Target Solutions offers services that may cover environment diagnosis, initiative inventory, maturity assessment, governance definition, process structuring, architecture design, integrations, observability, and operating model. When it makes sense for the environment, Target Solutions can also support implementation and integration of a platform such as ARGUS.
Learn about Target Solutions services for AI agents and talk with us about how to structure this journey in your organization.
About the author
Paulo Florêncio Santos de Menezes is partner and co-founder of Target Solutions, with work in infrastructure, monitoring, observability, automation, IT operations, and AI agent governance.
He holds a degree in Data Processing from Universidade Federal do Amazonas, an MBA in Business Management from Fundação Dom Cabral, and a Professional Master’s in Economics from Fundação Getulio Vargas.
In his Master’s research, he developed IBEOP-IA (Brazilian Index of Occupational Potential Exposure to Artificial Intelligence), investigating the potential exposure of Brazilian occupations to AI capabilities through the combination of occupational data, artificial intelligence patents, and natural language processing techniques.
References
[1] Deloitte. Business and IT leaders report AI agents are scaling faster than their guardrails. 2026.
[2] NIST. Artificial Intelligence Risk Management Framework and Generative Artificial Intelligence Profile.
[3] PwC. AI agents as workforce counterparts: what governance should look like. 2026.
[4] Boston Consulting Group. Trust Imperative 5.0: Governing AI at Scale. 2026.
[5] Deloitte. Agentic AI: Design for scale or prepare to fail. 2026.
[6] PwC. As AI agents take on more work, trust should become operational. 2026.